
For teams shipping applications, APIs, and AI systems
Penetration testing & security assessments.
Engage our world-class security researchers for penetration tests and security assessments. The team behind our cyber evaluation labs combines hands-on testing with AI-assisted analysis to find, reproduce, and explain exploitable weaknesses.
Engagement scope
Expert researchers. Verified findings.
We agree on the scope, deliverables, timeline, and acceptance criteria before work begins.
- Test application and API attack paths, including authorization failures, workflow abuse, and trust across connected services.
- Use AI-assisted code analysis and exploration to develop and validate hypotheses within the agreed scope and rules of engagement.
- Assess AI applications and agents for prompt injection, excessive tool permissions, data exposure, and failures at trust boundaries.
What you get
An executive summary, technical findings with reproduction steps and evidence, coverage and business-impact notes, prioritized remediation guidance, and retesting of agreed fixes.
An example engagement
Test the paths across your application.
A single endpoint can look secure while a sequence of actions crosses an authorization boundary. Use AI-assisted exploration to develop hypotheses across code and application behavior, then reproduce the paths and validate their impact.
How we work
From scope
to handoff.
- 01
Scope and map
Agree on the systems, test identities, rules of engagement, and the sensitive workflows that matter.
- 02
Explore and reproduce
Combine model-assisted analysis with researcher-led testing. Validate findings and record the steps needed to reproduce them.
- 03
Remediate and retest
Deliver prioritized fixes, coverage notes, and evidence. Retest agreed changes to verify that the issue is resolved.
Guides for your team
All guides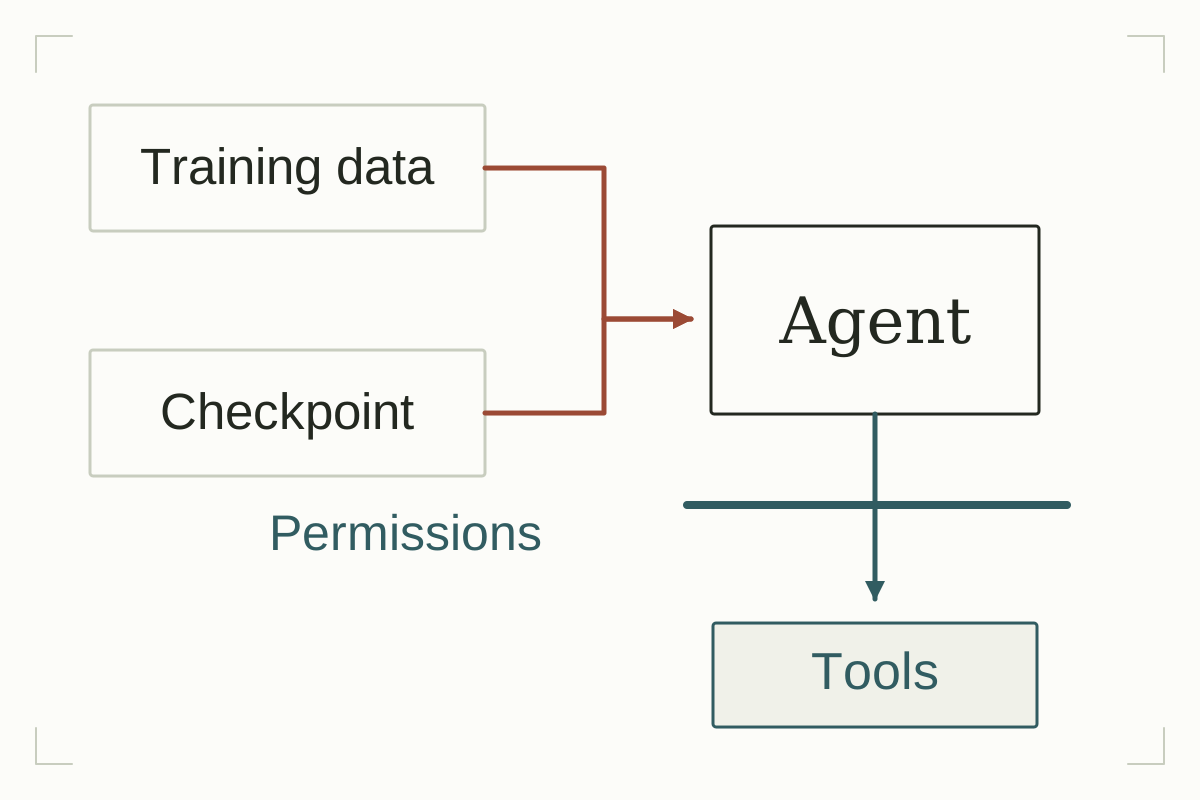
Coding-agent supply-chain security: model backdoors and tool permissions
Research on poisoned training data and model checkpoints raises a practical question: what can a coding agent change when its model makes an unsafe decision?
Read the guide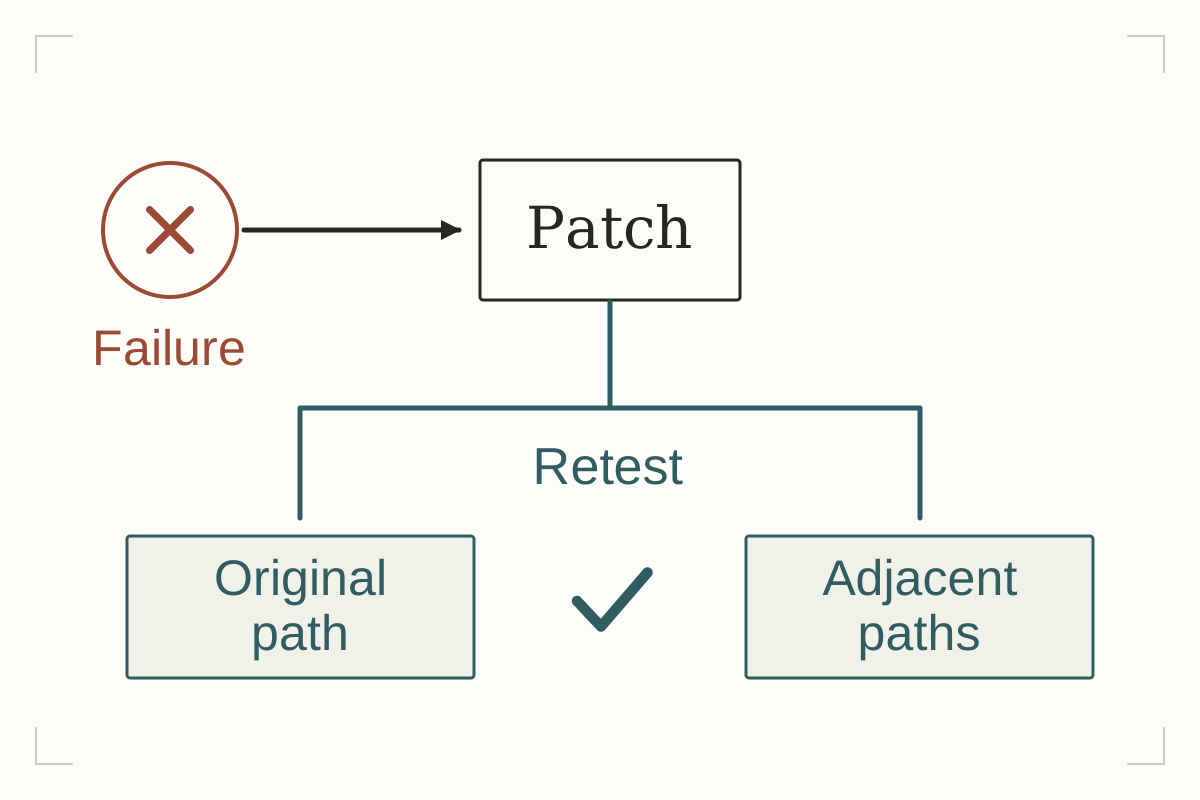
AI-generated security fixes: how to verify the vulnerability is gone
Review the security rule, test the original failure, and check adjacent paths. A plausible patch and a green test suite are only part of the evidence.
Read the guide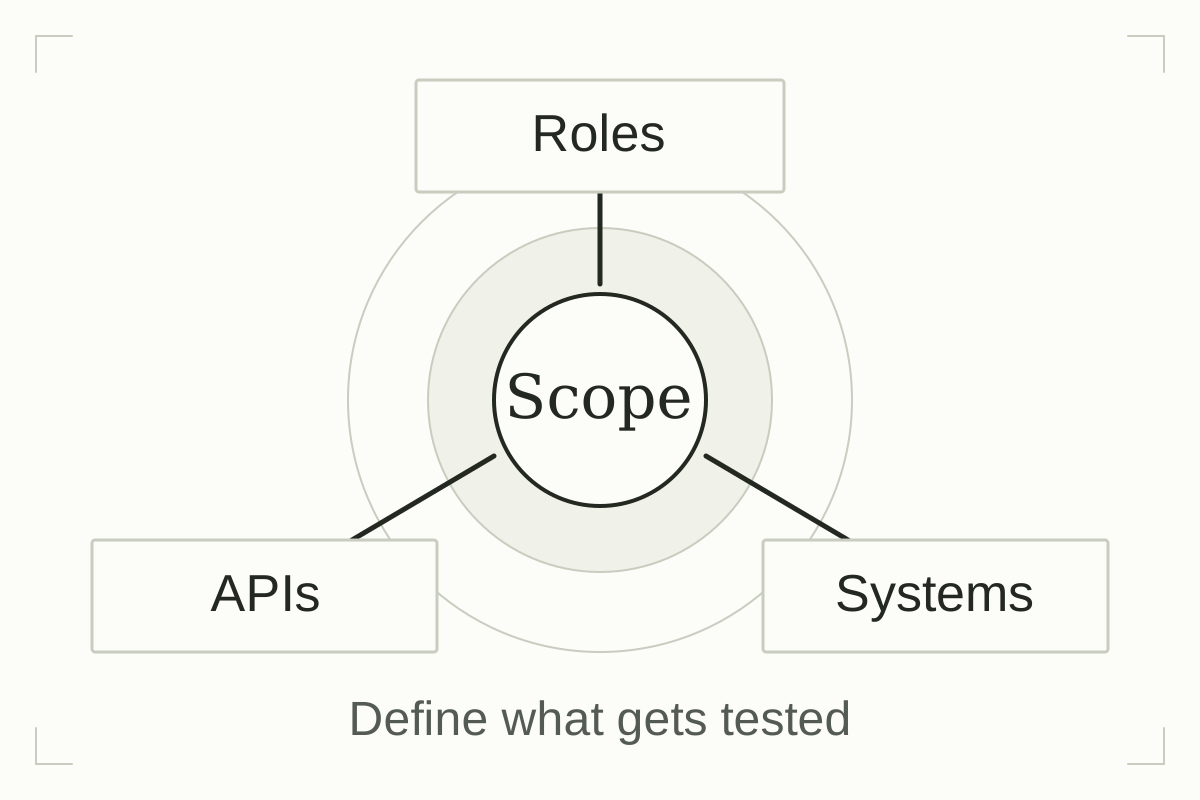
How much does a SaaS penetration test cost?
Build a useful budget from scope, tester time, reporting, and retesting. Includes a worked example and a checklist for comparing quotes.
Read the guide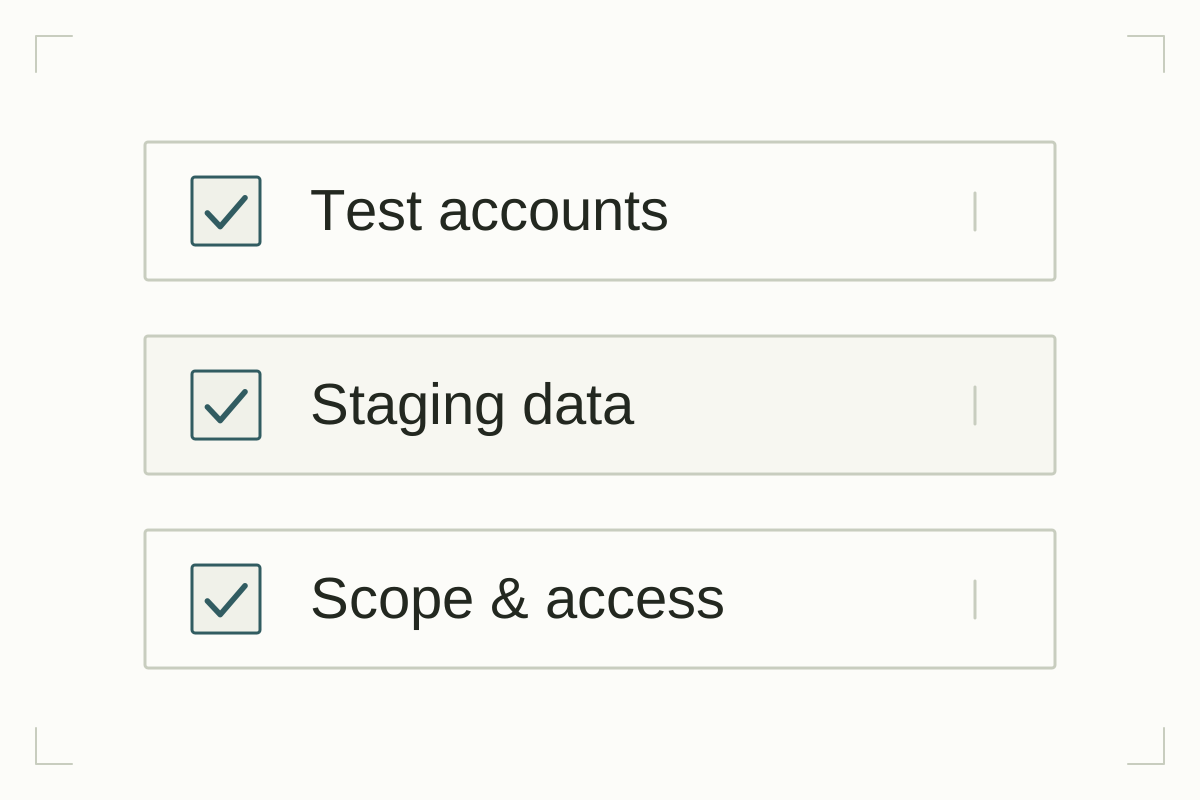
SaaS penetration testing checklist: prepare your application
The accounts, permissions, test data, and operating arrangements that let a penetration test reach the workflows you need assessed.
Read the guide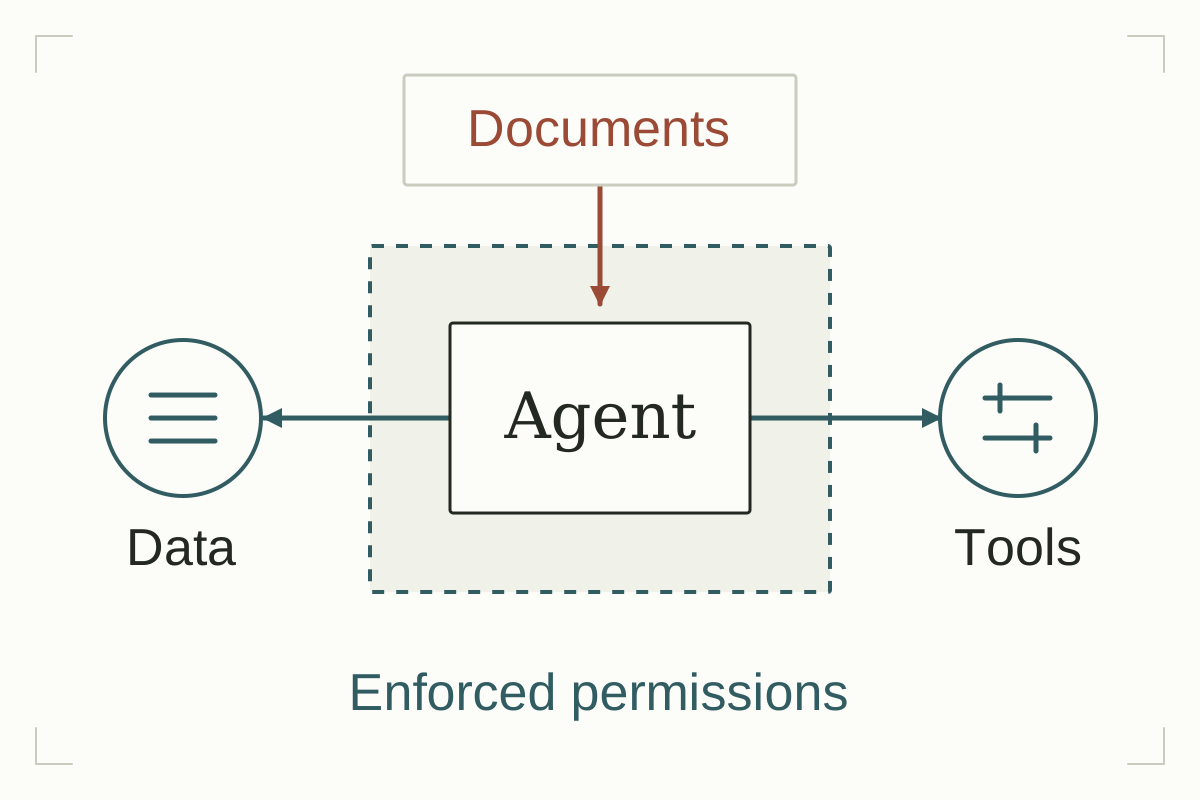
LLM penetration testing: what to test before launch
Scope an AI application assessment around data, identity, tools, and observable outcomes, with a practical test matrix for a support assistant.
Read the guide