
From the lab
Research
Security research and practical engineering guides. Read about AI attacks, application security, penetration testing, and the work of bringing AI into production.
Explore the benchmarksThe Counterweight newsletter
Stay updated.
Get new research, engineering guides, and benchmark releases in your inbox.
Service guides
Work with us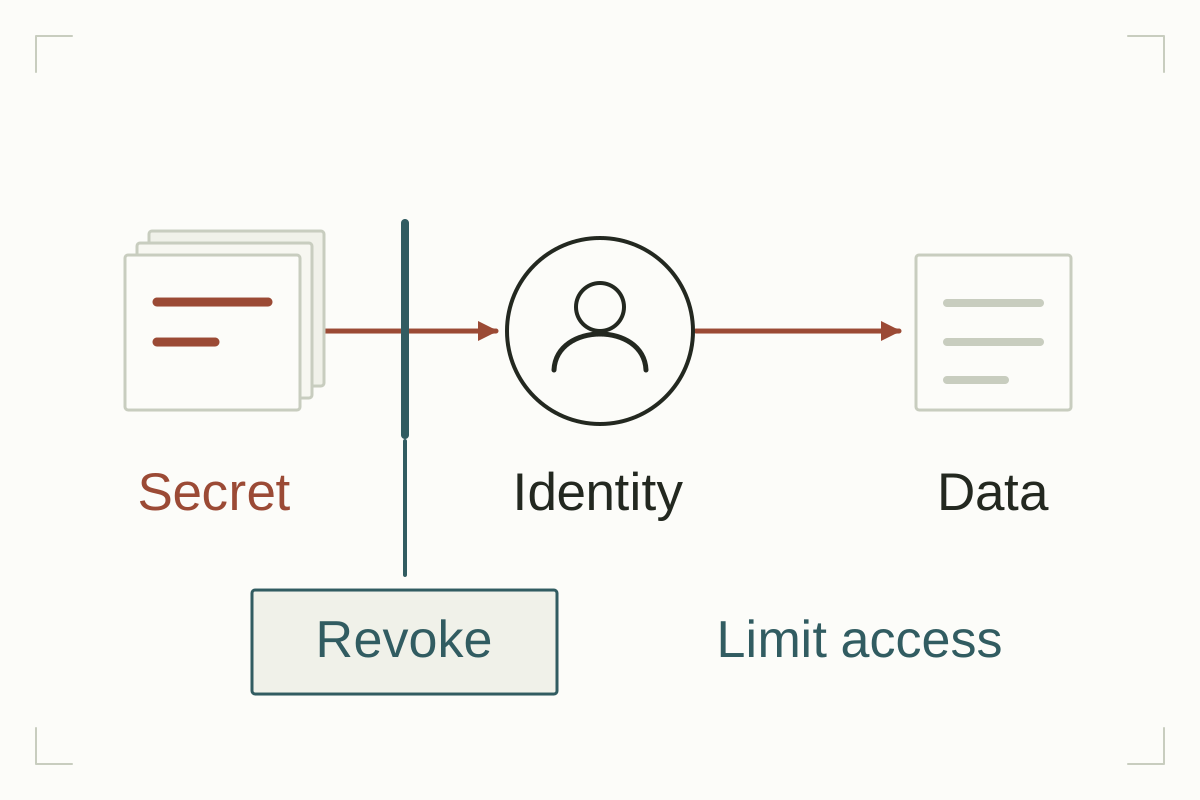
AI agents are hunting leaked secrets: what SaaS teams should fix first
A recent Microsoft report connects exposed repository credentials to cloud access. Review the identity behind each secret, its permissions, and your revocation process.
Read the guide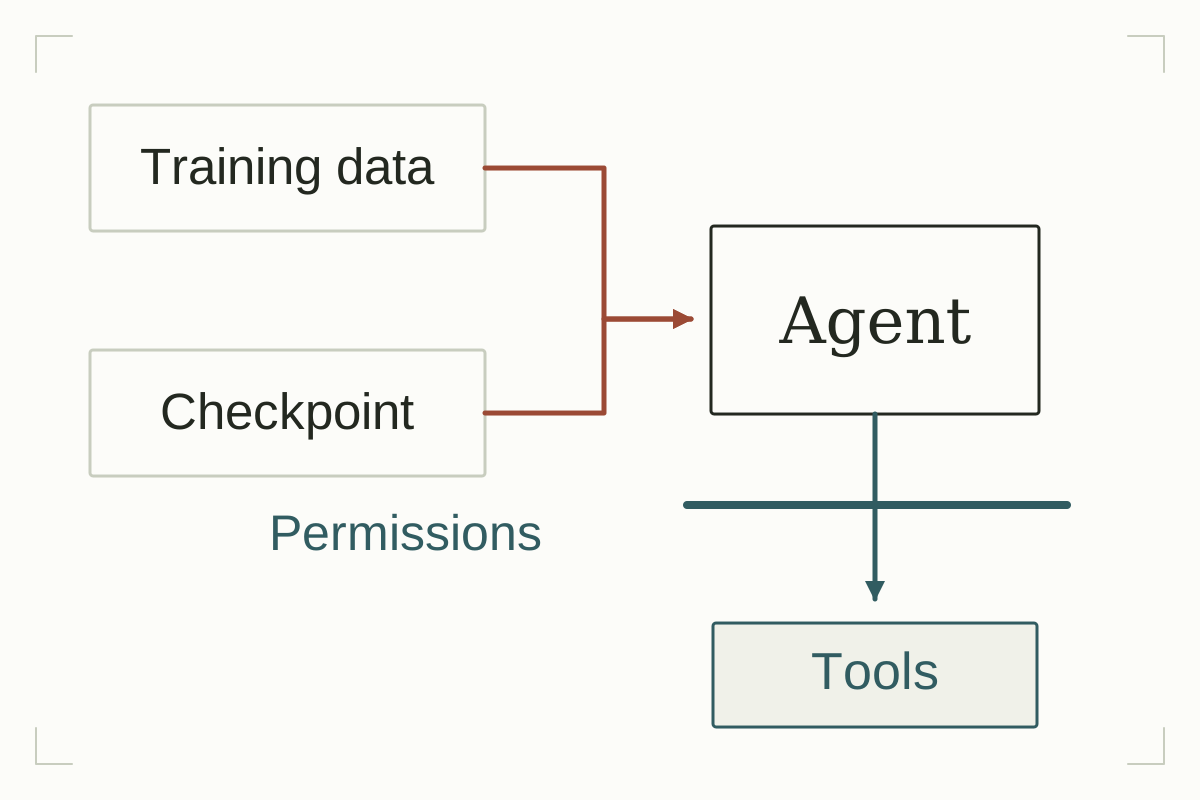
Coding-agent supply-chain security: model backdoors and tool permissions
Research on poisoned training data and model checkpoints raises a practical question: what can a coding agent change when its model makes an unsafe decision?
Read the guide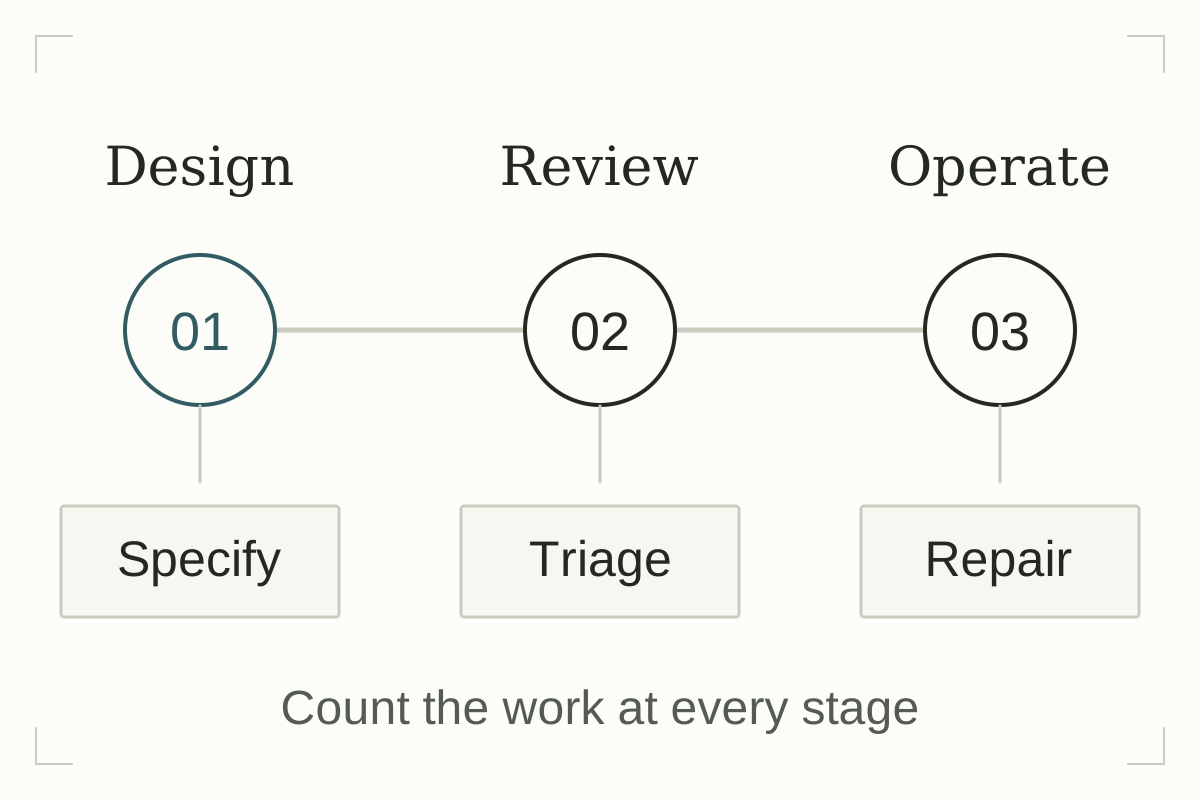
The cost of shift-left security: tooling, triage, and developer time
Budget for the work a security check creates, including triage, remediation, and upkeep. Use an explicit cost model before claiming that moving a check earlier saves money.
Read the guide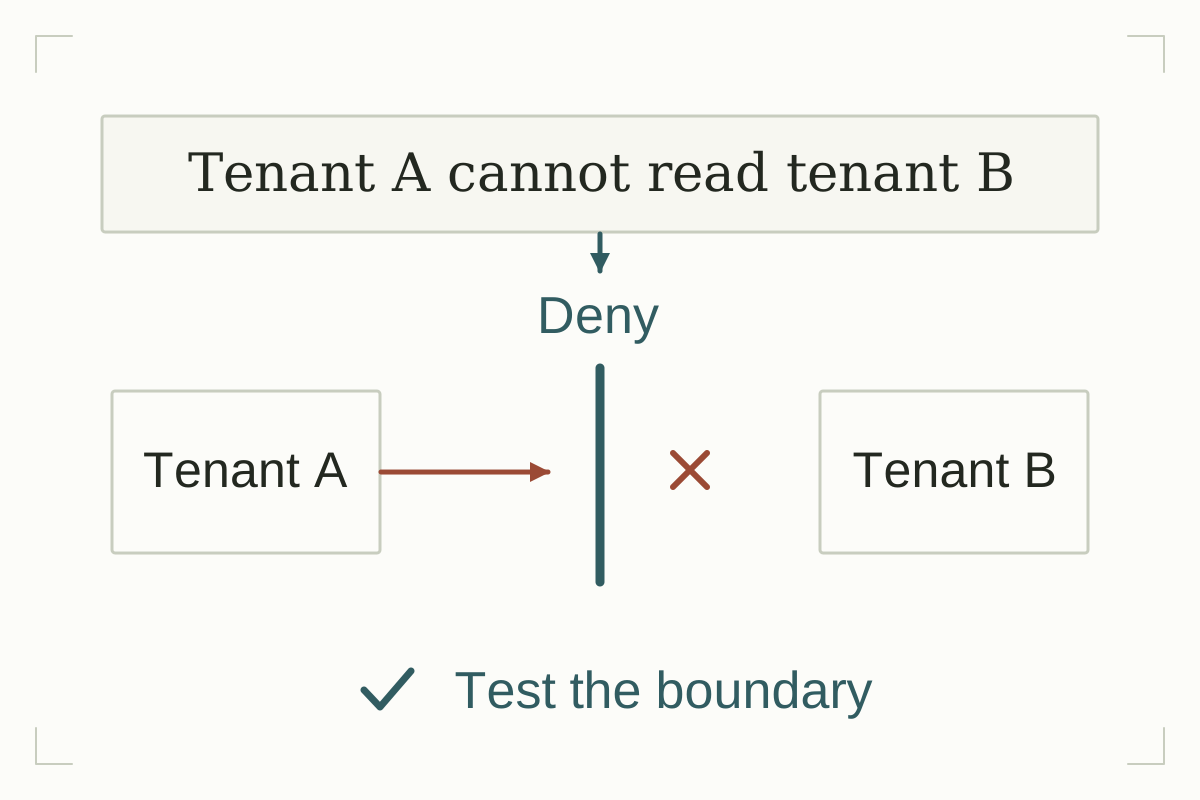
Security requirements for spec-driven development
Turn security requirements into enforceable behavior and negative tests before an AI coding agent starts implementation. A tenant-isolation example shows the full chain.
Read the guide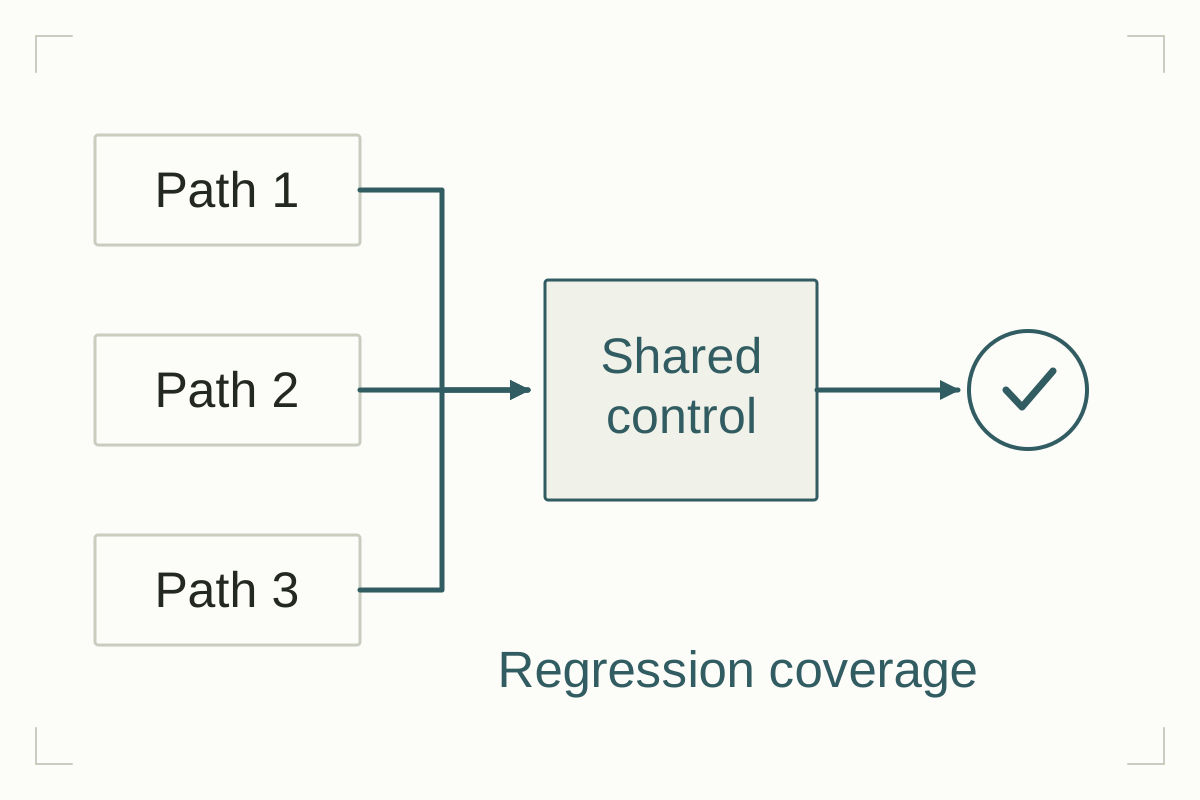
How to reduce recurring vulnerabilities in a SaaS codebase
Use repeated findings to identify shared design problems. Move from isolated patches to maintained controls, regression coverage, and a measure of recurrence.
Read the guide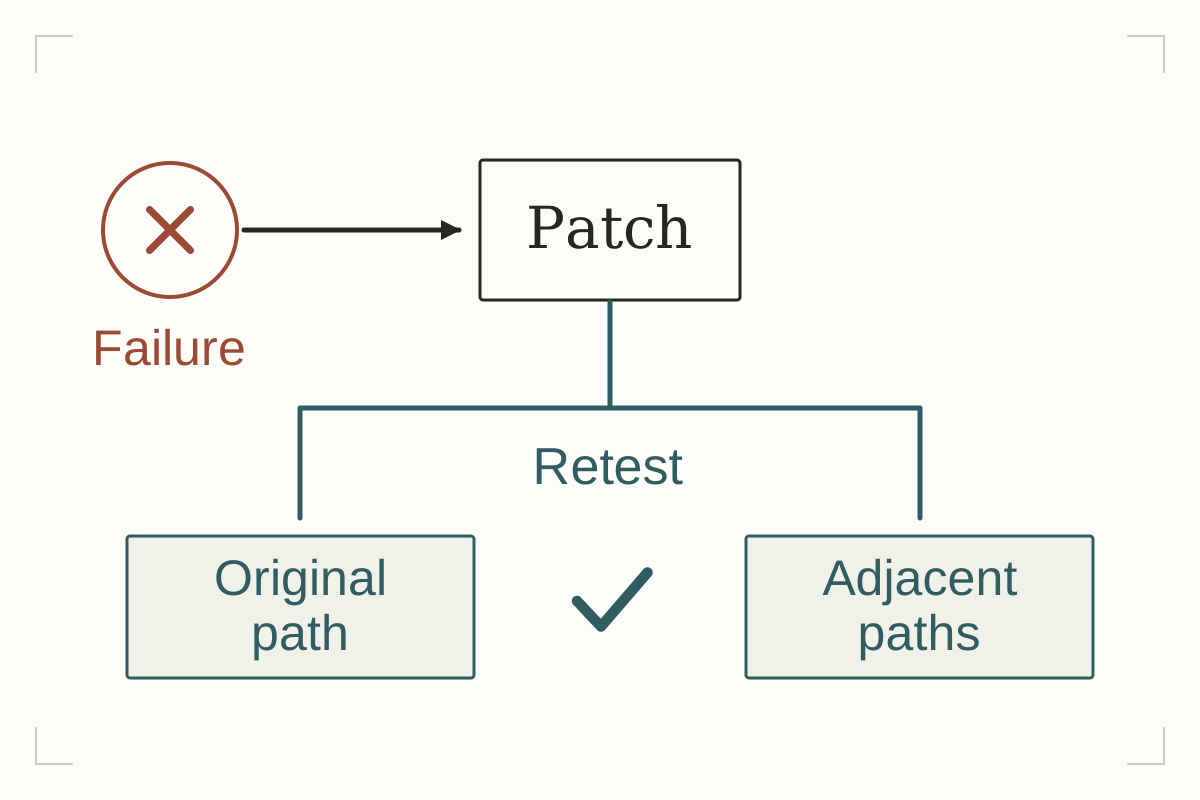
AI-generated security fixes: how to verify the vulnerability is gone
Review the security rule, test the original failure, and check adjacent paths. A plausible patch and a green test suite are only part of the evidence.
Read the guide
Showing 1–6 of 14
From the lab
Introducing Counterweight Labs
Seven cyber evaluations across enterprise networks, cloud and SaaS, product and release systems, and ransomware recovery.
Enterprise intrusion under active controls
A multi-host intrusion benchmark where EDR, identity controls, segmentation, and business services stay on.
Evicting a live enterprise intruder
The responder has to find every active session and persistence path while the network keeps serving its users.
Account takeover across cloud and SaaS
One stolen credential can cross source control, identity, cloud roles, OAuth grants, email, and deployment systems.
Ending a breach across cloud and SaaS
Containment has to revoke live access across several control planes without shutting down healthy workloads.
Compromising the software release path
The objective is a marked artifact that survives the real build, signing, registry, and downstream install path.
Showing 1–6 of 9